Master security. Don’t just document it.
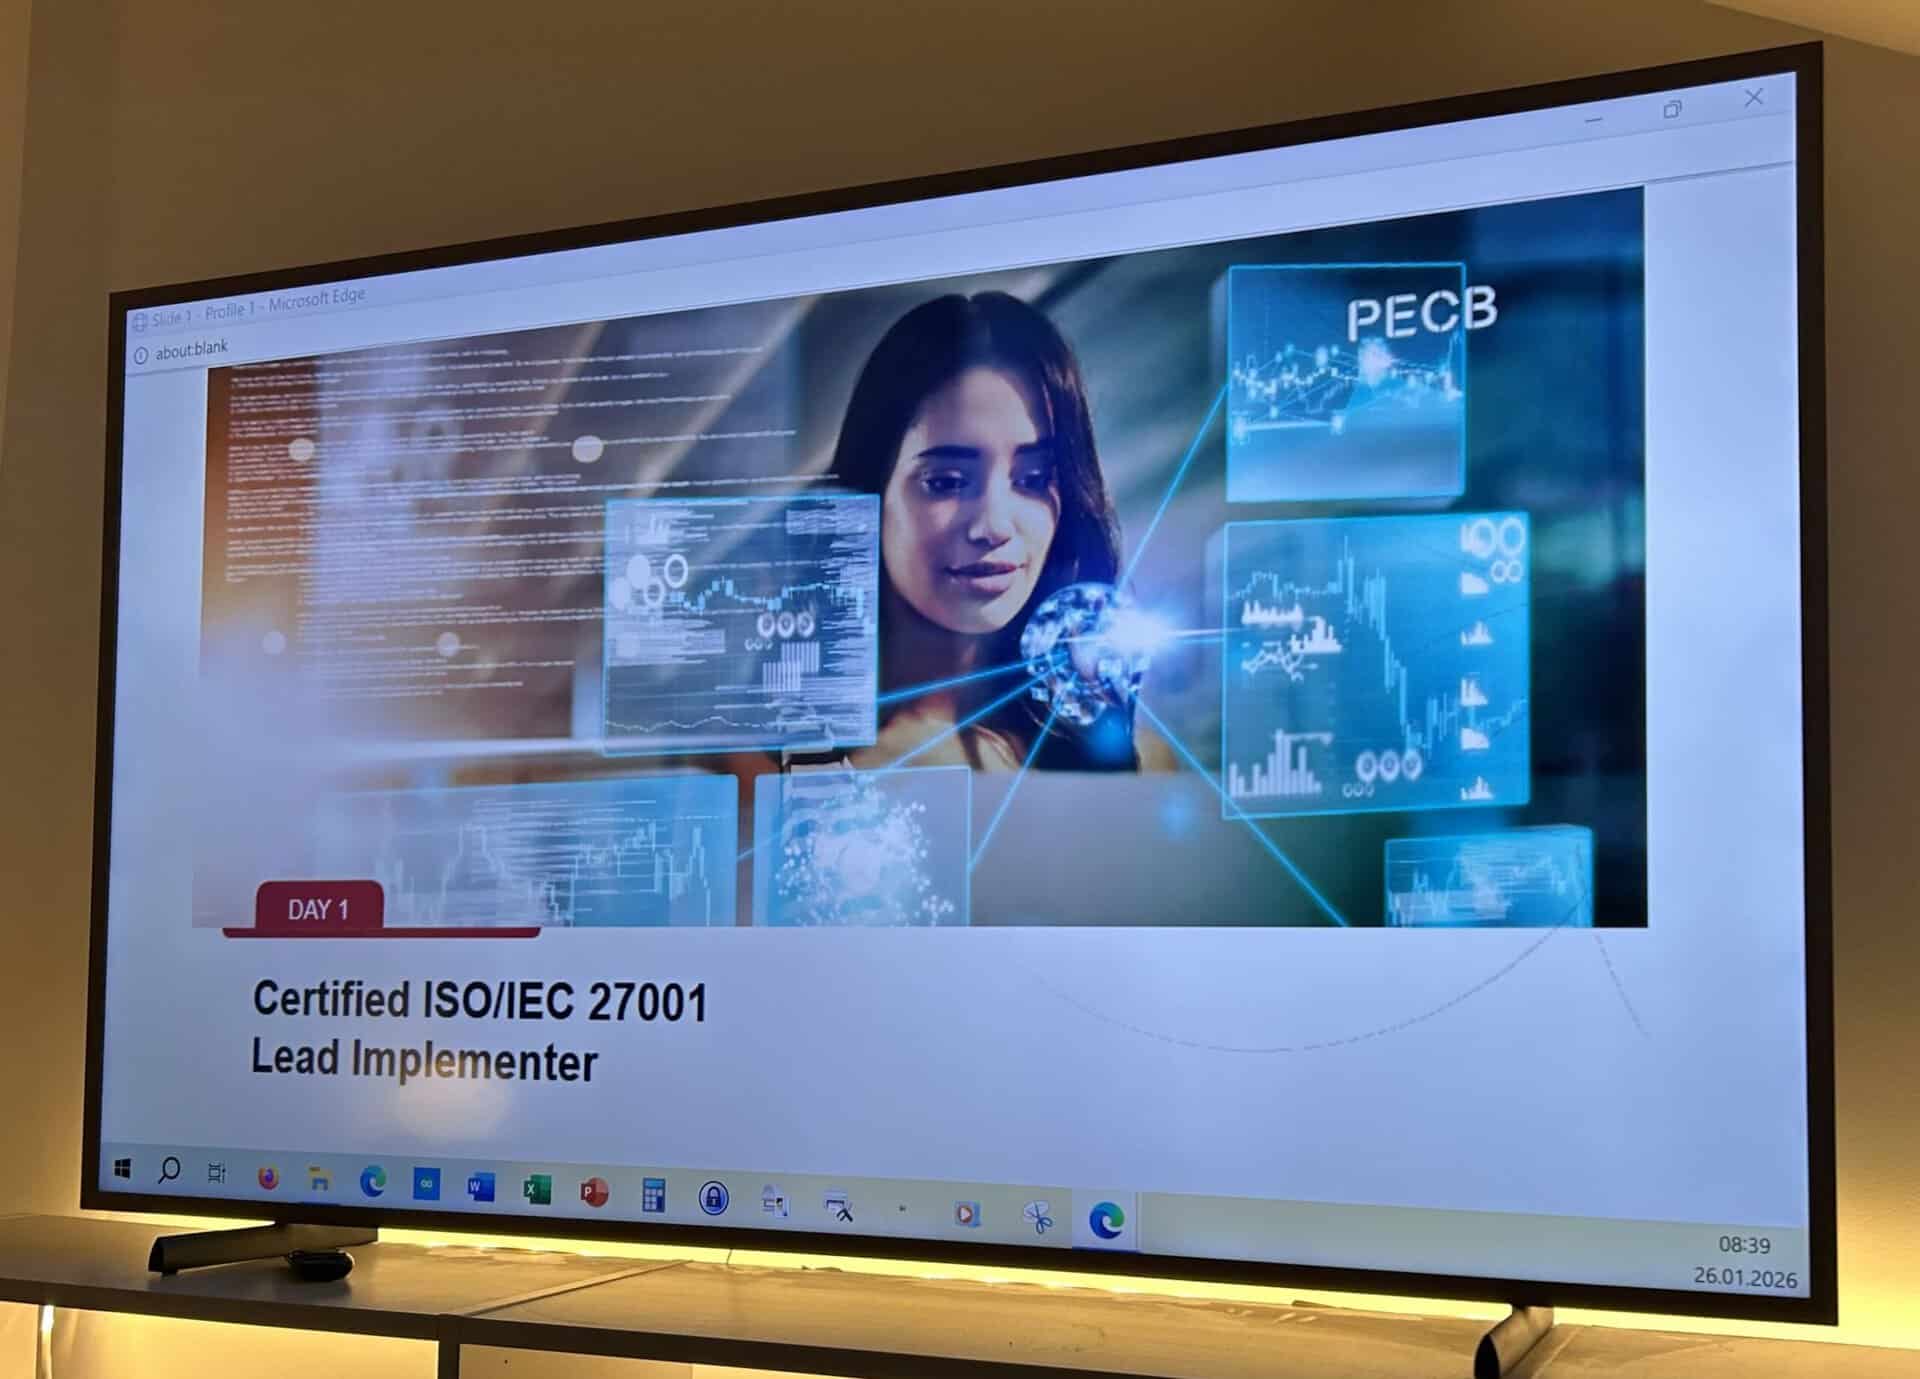
In January, Cybexpert delivered a session dedicated to the implementation and management of ISO/IEC 27001, bringing together cybersecurity managers and professionals involved in certification or continuous improvement initiatives.
The discussions focused in particular on:
- Adapting ISO 27001 requirements to the specific context of organisations
- Risk management as a management tool, rather than a mere documentation exercise
- The strategic role of the CISO in discussions with senior management
As is often the case, a shared observation emerged: the difficulty lies not in understanding the standard, but in applying it consistently and sustainably.
Discussions between participants from a variety of sectors helped broaden perspectives and illustrate the real-world challenges encountered in practic
Thank you to all participants for the quality of the discussions and their engagement.
Upcoming sessions are available in the Training section.